
GDPR
PaperOffice meets the GDPR requirements for processors — DPA (Art. 28) and TOMs (Art. 32) from the generator, processing in the EU.
- Data processing in the EU
- Right to deletion
- Transparent processing


Choose language
Select currency
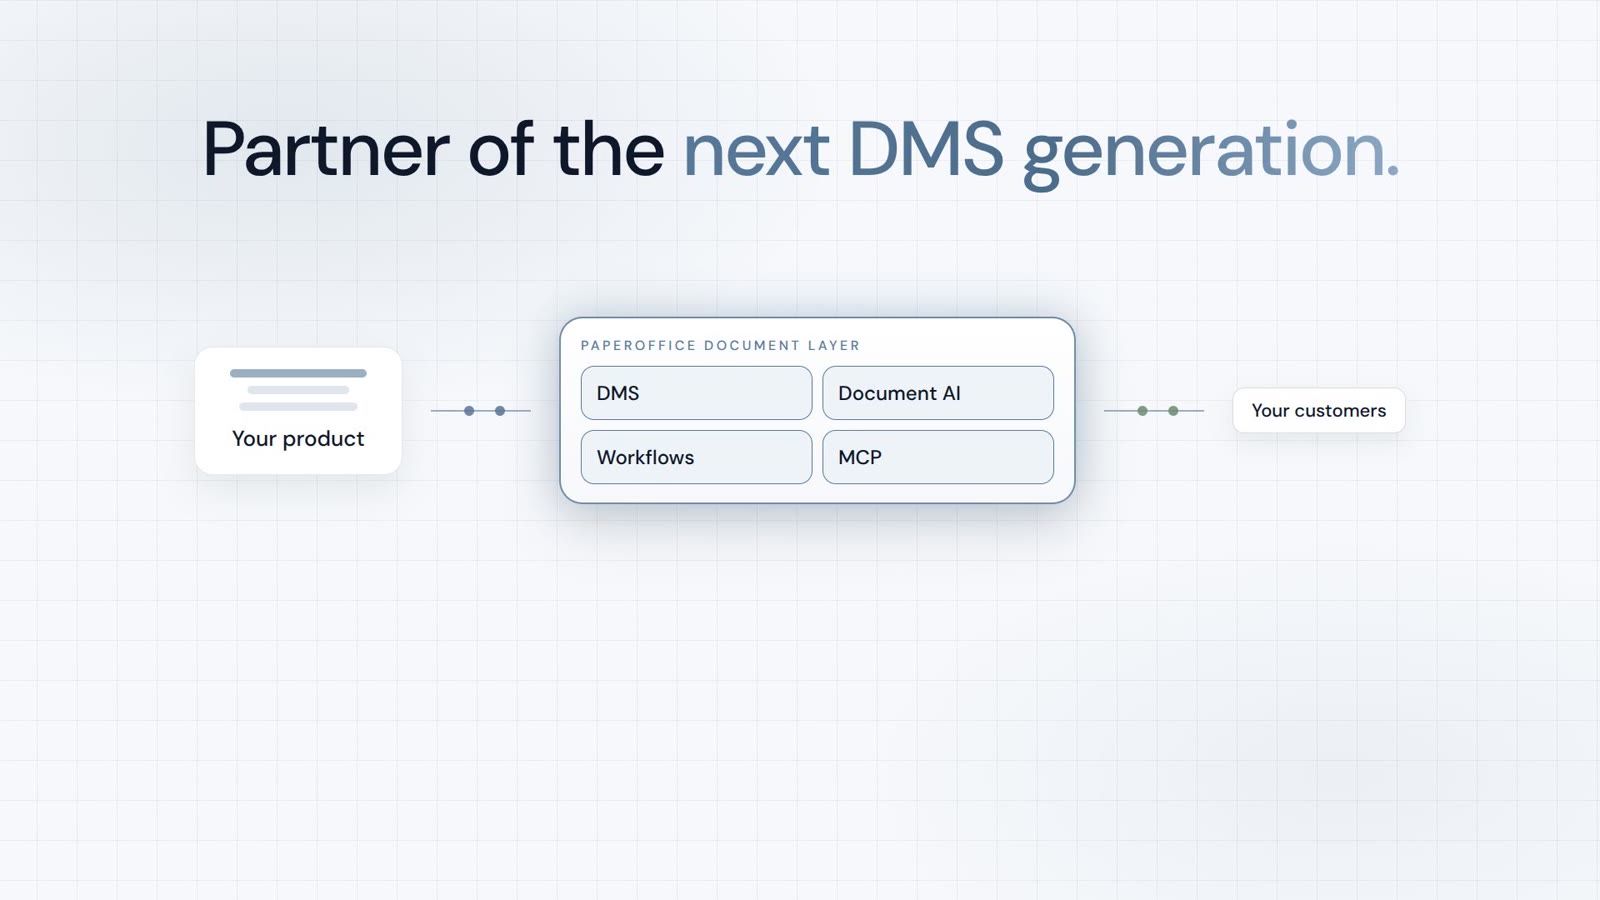
Integrator and Reseller can be combined. Referral by invitation.
View the partner program
Security & Compliance
DPA, TOMs and ISO/IEC 27001 certificate — documented, not merely claimed.
Trusted by leading companies worldwide
OEM PARTNERSHIP
Sole official DMS partner for QNAP: Classic app, AI BYOS.
More
Sole official DMS partner for ASUSTOR: Classic app, AI BYOS.
MoreProof
Processing on own hardware in the EU Datacenter Spain. The generator produces the DPA and the TOMs — from company data, as a PDF.
Documented standards: GDPR requirements for processors met, ISO/IEC 27001 certified; SOC 2 Type II in preparation.
PaperOffice meets the GDPR requirements for processors — DPA (Art. 28) and TOMs (Art. 32) from the generator, processing in the EU.
International standard for Information Security Management
AICPA Service Organization Control for Trust Services Criteria
US standard for health data — PaperOffice meets all technical safeguard requirements of the HIPAA Security Rule.
Card payments run through Stripe Checkout. Card details are entered at Stripe and do not reach PaperOffice servers.
Technical building blocks for record-keeping under the GoBD (German bookkeeping rules)
ISO/IEC 27001 certified (certificate available under NDA); SOC 2 Type II in preparation.
Encryption
Every document is stored encrypted with AES-256 and transmitted over TLS 1.3.
All stored data fully encrypted
TLS 1.3 for all connections
Keys stored outside the database — readable only by authorised services
Decryption only for authorized processing – with audit trail
Every request is authenticated. Every access is logged. No exceptions.
Multi-factor authentication, passkeys and Google sign-in; code challenge for new devices and unusual networks.
Minimal permissions. Only access to what's really needed.
Permanent verification. No "trusted zones". Every session is validated.
Complete logging of all access. Immutable audit logs.
Isolated network segments. Breach in one area stays isolated.
Alerts for logins from new devices, new IP addresses or VPN, proxy and data-centre networks. “No, this was not me” locks the account and ends all sessions.
Trust Center
The generator in the app produces the DPA and the TOMs — from company data, as a PDF.
The data processing agreement is created in the app — pre-filled with the company data, as a PDF on PaperOffice letterhead.
Technical and organisational measures for exactly the services used in the account.
All devices and sessions of the account at a glance — who accesses what, when and from where.
Per device, the countries from which access is permitted are defined. Regions not approved are blocked.
PaperOffice runs its own EU infrastructure. Against DDoS attacks and bots, PaperOffice uses Cloudflare Enterprise as network protection — with no access to documents.
DDoS Protection & CDN
Databases, storage, AI models and backup systems run on our own hardware in the EU Datacenter Spain.
Whitepaper, penetration-test report and the ISO/IEC 27001 certificate are available on request from the Enterprise plan.

